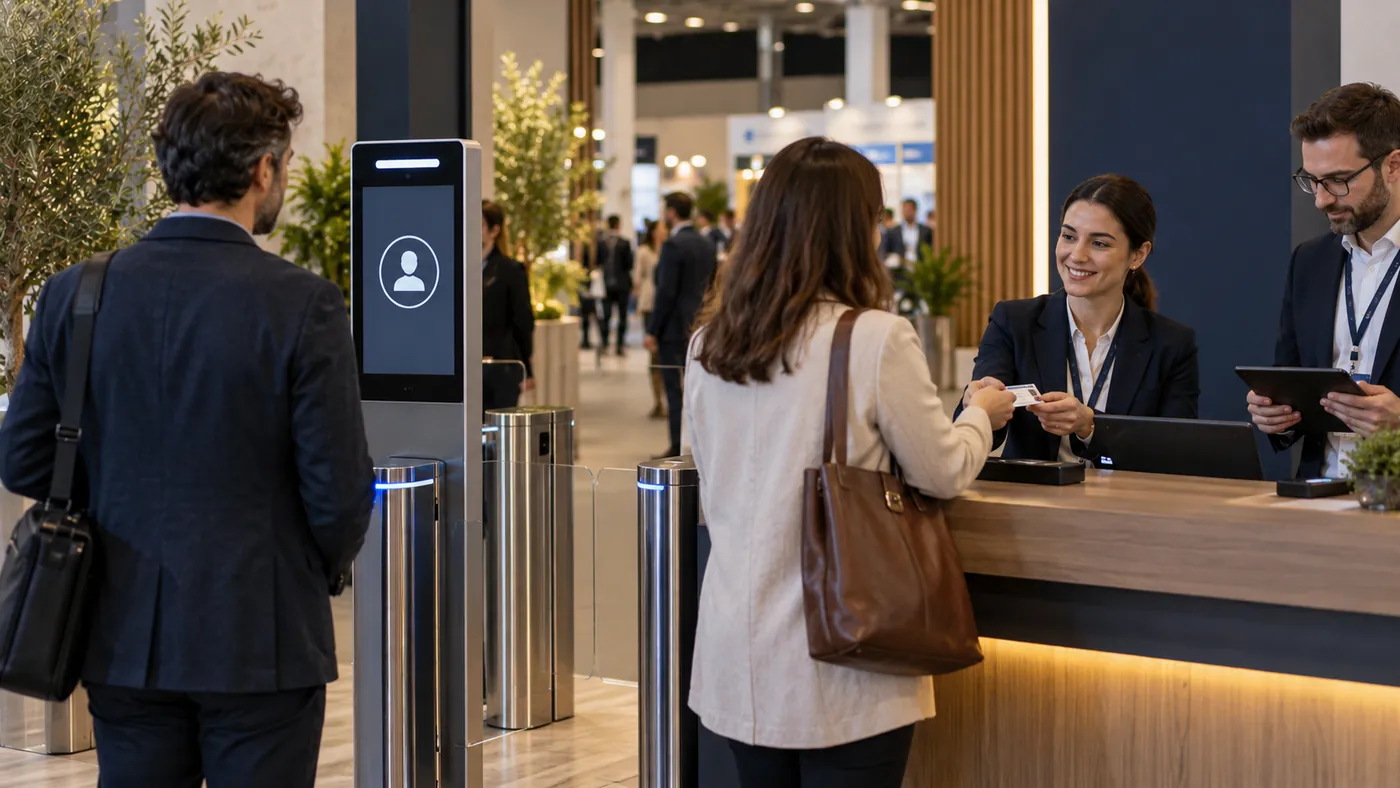
Major exhibitions are increasingly introducing smart-entry systems based on facial recognition, fingerprints and other biometric information to reduce queues and strengthen security. MWC, the Mobile World Congress and the world’s largest mobile exhibition, likewise introduced facial-recognition entry at its 2021 event.
The outcome, however, was severe. In 2023, Spain’s data protection authority, AEPD, imposed a €200,000 fine, approximately ₩300 million, because MWC’s data protection impact assessment was inadequate. From an event planner’s practical perspective, this was more than a matter of collecting too few consent forms. As the procurement and admission-control principles in "Case Article Review" also warn, introducing fast, impressive technology at the front end must be preceded by operational design that carefully separates and controls the legal risks and data pipelines behind it.
1. Decouple the functions: identity checks and biometric collection are different
A system-hire supplier may offer planners an all-in-one solution that handles everything once a photograph is uploaded.
- Break down the collection purposes: The event lead should nevertheless commission clearly separated technical responsibilities, establishing whether the system merely checks identity or stores and matches facial data on a server. In the MWC case, the organiser said facial recognition was optional, but an expert invited as a speaker revealed that she had been required to upload a passport copy for identity verification. Presenting identity checks and biometric storage as a mixed process can seriously undermine trust and lead to legal disputes.
2. Do not treat compliance documents as a formal cut-off
Handling personal information at scale requires an advance assessment of the risks—a data protection impact assessment.
- Substantive risk management: MWC submitted an assessment to the regulator, but it was found to have effectively copied an earlier year’s document and inadequately recorded the risk as zero. The planning team should not prematurely close the issue simply because a supplier has provided paperwork saying the system is safe. Before the event, an internal legal team or designated privacy lead should cross-check the purposes of collection, storage methods and rights safeguards against the actual on-site circumstances and provide sign-off.
3. Measure and rehearse the alternative admission route
Planners must have full control over what happens on site when a visitor opts out of facial recognition.
- Operate a separate failover desk: Even if a manual identity-check desk is available for visitors who do not wish to use the system, a very long queue or staff repeatedly insisting that registering through the app is faster can amount to coerced consent in practice. During the dry run, measure not only the throughput of visitors who agree to facial recognition, but also the turnaround time of the alternative route in which those who decline obtain an admission badge at the desk using only physical identification. Reallocate information staff on the basis of those measurements, down to the second.
4. A four-stage protocol for biometric entry systems
When planning a fast-entry system using facial recognition or other biometric data, the practical team should follow these four stages.
| Stage | Operating standard |
|---|---|
| Stage 1: Apply minimum-data procurement rules | From the supplier-proposal stage, remove unnecessary functions such as retaining original passport copies and require a data-minimisation architecture that deletes information as soon as identity verification is complete. |
| Stage 2: Establish explicit consent and a bypass | When designing ticketing and registration interfaces, clearly separate biometric provision as optional rather than mandatory, and explain that visitors who decline can enter through the offline desk without disadvantage. |
| Stage 3: Hand over on-site staff responsibilities | Prohibit prompts that steer visitors towards registering for facial recognition to enter faster. Train information staff in scripts that direct those who decline quickly and courteously to the manual desk. |
| Stage 4: Obtain sign-off on complete data purging | Immediately after the event, obtain a destruction certificate from the supplier confirming that all biometric information and identity-document copies temporarily stored on the hired system’s servers have been permanently deleted, bringing the legal responsibility to a close. |
Planner’s memo: advanced technology’s speed is safe only within conservative rules
The sight of visitors walking through a gate without stopping is highly appealing to an exhibition planner.
Yet that one second of convenience does not justify taking on the enormous, unprotected risk of tens of thousands of people’s biometric data. When introducing new IT at an event, the first document a planner should open is not the supplier’s glossy brochure. It is the rigorous legal review setting out the event’s security rules and personal-data destruction manual. Truly safe, fast admission is achieved through the planner’s conservative controls that carefully remove even unlikely risks, rather than through the spectacle of the technology.
Conditions for applying this elsewhere
Relevant when biometric features are proposed for event registration or access. Applicable laws and the actual processing require a separate review.
Information not established
The original sanction PDF could not be opened; the sanction and grounds were cross-checked against the official reconsideration decision and 2023 Annual Report. Payment, the final outcome of any subsequent court proceedings and the current system’s legality were not verified. Separate health-data cases in 2024 are not combined with this sanction.
Reference material
- GSMA · MWC21 post-event release (6 July 2021)
- GSMA · MWC21 date-change announcement (23 September 2020)
- AEPD · 2023 Annual Report, printed pages 95–96 (PS/00553/2021)
- Business Insider España · Interview with the complainant (9 May 2023)
- AEPD · Administrative reconsideration decision EXP202100603 (initial sanction: 24 February 2023)
- GSMA · Official statement on the AEPD decision (9 May 2023)
Have a correction or additional evidence? Request a correction